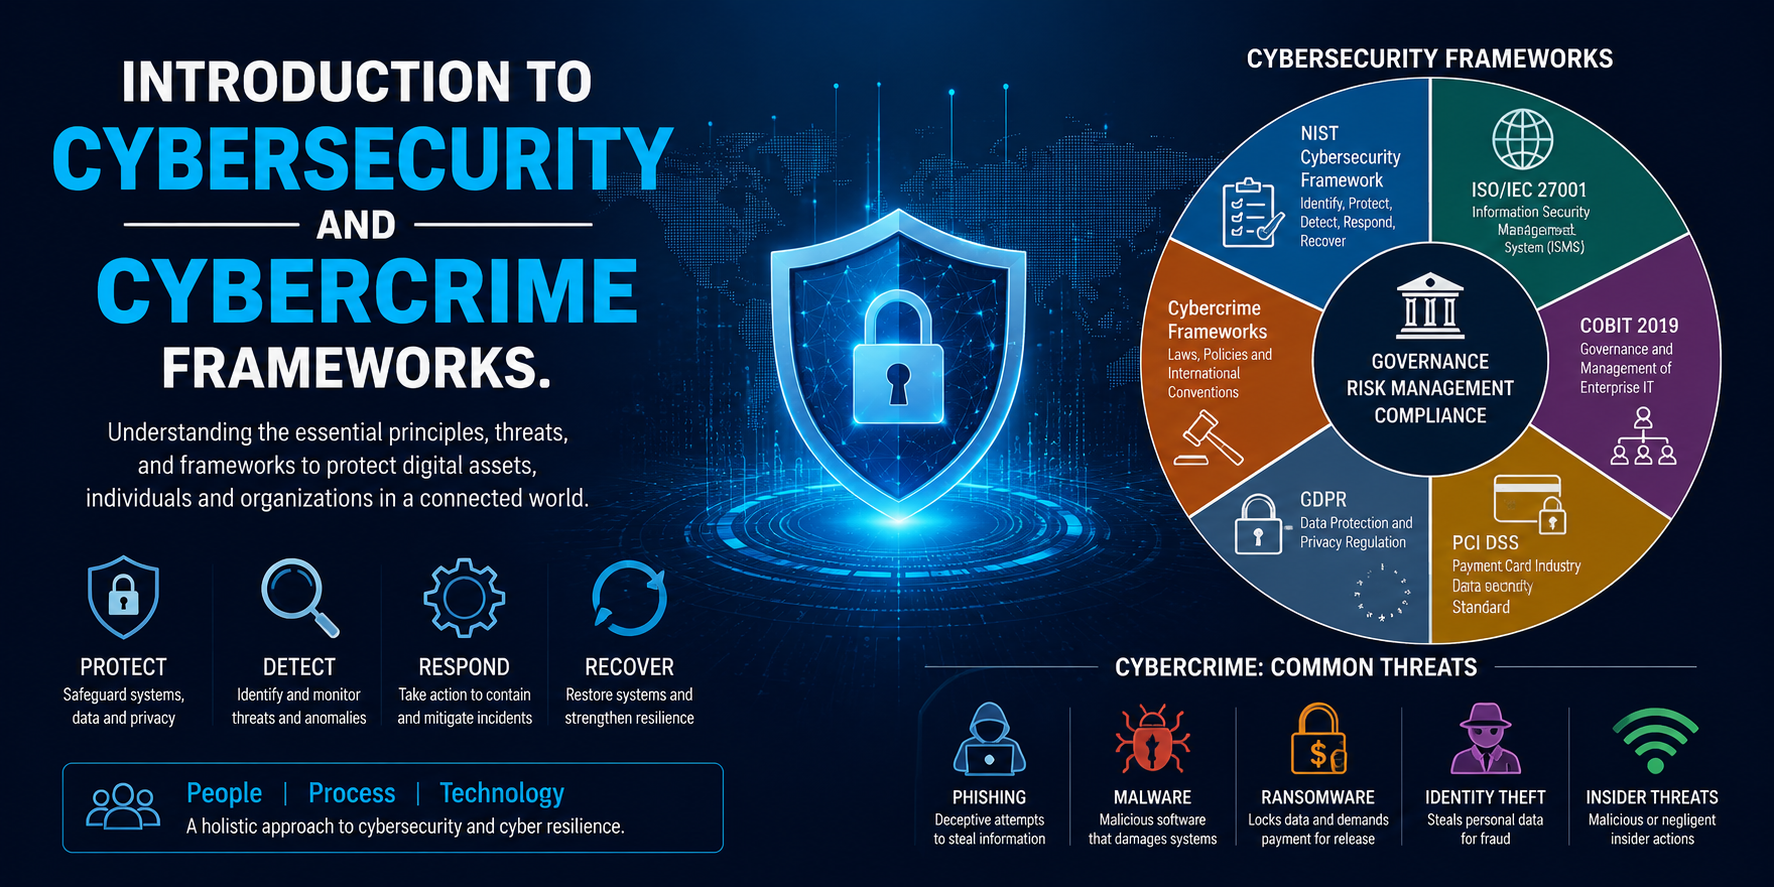
Introduction to Cybersecurity and Cybercrime Frameworks.
Understanding cybersecurity and cybercrime requires looking at two distinct but deeply connected domains: defensive governance (protecting systems and managing risk) and adversarial analysis/legal governance (understanding, preventing, and prosecuting illicit activities online).
Frameworks provide the standardized blueprints, taxonomies, and legal structures that allow organizations, law enforcement, and policymakers to coordinate globally.
1. Core Cybersecurity Defensive Frameworks
Defensive frameworks give organizations structured guidelines to assess risk, implement security controls, and respond to incidents.
NIST Cybersecurity Framework (CSF 2.0)
Published by the National Institute of Standards and Technology, CSF is the global benchmark for organizational security, built around six core functions:
-
Govern: Establishing policy, roles, and enterprise risk management strategy.
-
Identify: Mapping assets, systems, data, and organizational risks.
-
Protect: Implementing safeguards like access control, encryption, and awareness training.
-
Detect: Monitoring systems for anomalies and security events in real time.
-
Respond: Executing incident response plans to contain threats.
-
Recover: Restoring operational resilience and systemic functionality after an attack.
ISO/IEC 27001
An international standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). While NIST CSF offers a flexible outcomes-based framework, ISO 27001 provides formal certification requirements based on rigorous risk assessments and technical controls.
2. Cybercrime & Adversarial Threat Frameworks
Understanding how threat actors operate allows defenders to anticipate tactics, map attribution, and disrupt malicious infrastructure.
MITRE ATT&CK®
A globally accessible knowledge base of adversary tactics, techniques, and procedures (TTPs) based on real-world observations. It breaks down cyberattacks into technical steps—from initial access and execution to lateral movement and exfiltration—providing a common lexicon for security analysts and threat intelligence teams.
The Cyber Kill Chain®
Developed by Lockheed Martin, this model traces the stages of a targeted cyberattack sequentially:
-
Reconnaissance $\rightarrow$ 2. Weaponization $\rightarrow$ 3. Delivery $\rightarrow$ 4. Exploitation $\rightarrow$ 5. Installation $\rightarrow$ 6. Command & Control (C2) $\rightarrow$ 7. Actions on Objectives.
3. Cybercrime Legal & Policy Frameworks
Because digital infrastructure spans physical borders, addressing cybercrime requires international cooperation, legal harmonisation, and multi-stakeholder governance.
The Budapest Convention on Cybercrime (Council of Europe)
The first international treaty seeking to address Internet and computer crime by harmonizing national laws, improving investigative techniques, and increasing cooperation among nations. It targets:
-
Offences against the confidentiality, integrity, and availability of computer data/systems.
-
Computer-related offences (fraud, forgery).
-
Content offences (child exploitation, illegal content).
-
Copyright infringements.
UN Cybercrime Convention
A globally negotiated UN legal instrument aimed at strengthening international cooperation to counter cybercrime, expanding access to electronic evidence, and establishing cross-border assistance channels between nation-states.
Summary Matrix
| Framework | Primary Focus | Key Audience | Primary Use Case |
| NIST CSF 2.0 | Defensive Governance | CISOs, Security Teams | Risk management & security maturity |
| ISO/IEC 27001 | Compliance & Auditing | Auditors, Enterprise Leadership | ISMS certification & operational standards |
| MITRE ATT&CK | Adversary Behavior | Threat Hunters, SOC Analysts | Detection engineering & threat mapping |
| Budapest Convention | Legal & Jurisdiction | Policymakers, Law Enforcement | Cross-border legal requests & prosecution |